Skip to content

City of Princeton cybersecurity incident

Summary

City of Princeton logo

The City of Princeton disclosed a cybersecurity incident in September 2026 affecting municipal systems and later confirmed theft of confidential and personal information. The city said essential services continued normally, while the public record does not establish whether other services or internal workflows were disrupted.

Key facts

Timeline

  • First public signal:
    ? Earliest public indication of an outage, disruption, closure or other observable incident impact. The signal does not need to mention cybersecurity.
  • First public cyber evidence:
    ? Earliest credible public information connecting the incident or disruption to malicious cyber activity.
  • Official cyber disclosure:
    ? First official acknowledgment by the affected organization or an authoritative public body that the incident was cyber-related.

Primary victim organization

Impacted locations

Critical infrastructure sector

Incident characteristics

Assessments

Attack mechanisms

Data impacts

  • Data theft or exfiltration

    Data was copied, transferred, downloaded, or otherwise removed from the affected environment by an unauthorized party.

Operational impacts

  • Unknown operational impact

    Available evidence does not establish whether the incident caused material operational or service disruption.

Extortion indicators

  • Public leak threat

    The actor explicitly threatened to publish or publicly release victim data or incident details.

  • Leak-site listing

    The victim was listed on a threat actor or ransomware data-leak site as an alleged target or nonpaying victim.

  • Countdown or payment deadline

    The actor imposed a deadline or public countdown before increasing the demand, publishing data, deleting keys, or taking another threatened action.

Incident narrative

Analyst assessment

DysruptionHub assesses with high confidence that the City of Princeton, Texas, experienced a cybersecurity incident involving unauthorized access and data theft. The city’s official statement, first published Sept. 18, 2026, described potential unauthorized access; its Oct. 5 update confirmed that confidential and personally identifiable information had been exfiltrated. The dates describe disclosure and investigative findings, not an established intrusion onset.

An INC Ransom listing documented by RansomLook names the city and its princetontx.us domain. GalaxyWarden’s Sept. 16 report places the external claim before the city’s announcement. The listing is an unverified claim; confirmed data theft does not establish INC Ransom’s responsibility or ransomware encryption.

Operational significance

The city’s emergency council notice, posted Sept. 20 for the Sept. 21 meeting, described intrusion into critical IT and communications systems and the need to consider emergency response, recovery and remediation. This establishes affected municipal systems and an urgent response, but does not identify a service outage, system shutdown, forced workaround or completed restoration.

The city’s continuity assurance concerns essential services. It does not establish normal operation of every internal system or municipal workflow. Operational disruption remains unknown: the available sources do not substantiate incident-linked interruptions to payments, telephone service, emergency response or other public services.

Confidence and uncertainty

Confidence is high in the city’s acknowledgment of data theft and medium in the external-first disclosure chronology, which rests on a dated secondary report and tracker listing. Confidence in INC Ransom attribution is low because no city finding or independent technical evidence connects that claimant to the confirmed theft. Ransomware or data-extortion involvement remains unresolved; NBC 5’s Sept. 22 reporting described an unnamed group’s publication threat and contact deadline, without establishing encryption, a ransom payment or an authenticated stolen-data corpus.

The city initially reported that two independent reviews found no breach evidence on Sept. 22, then confirmed exfiltration on Oct. 5 following continuing forensic review. The later finding supersedes the preliminary negative data assessment. The exact information taken and number of affected people remain unresolved.

In Oct. 8 reporting by the Princeton Herald, Bob Wieland described a resident’s Sept. 28 allegation that unauthorized purchases had been made with a credit card he had on file with the city. The report does not establish a causal link to the incident or confirm that payment-card information was stolen. The resident’s account of purported city data appearing online also remains unverified; it does not establish authenticated public disclosure of the stolen information.

Analytic gaps

The public record does not establish the initial access method, intrusion onset, compromised hosts or accounts, duration of unauthorized access, encryption, data volume, affected-person count, ransom demand or payment. It also does not establish whether containment restricted staff access, which workflows were delayed or when all affected systems returned to normal.

Disclosure posture

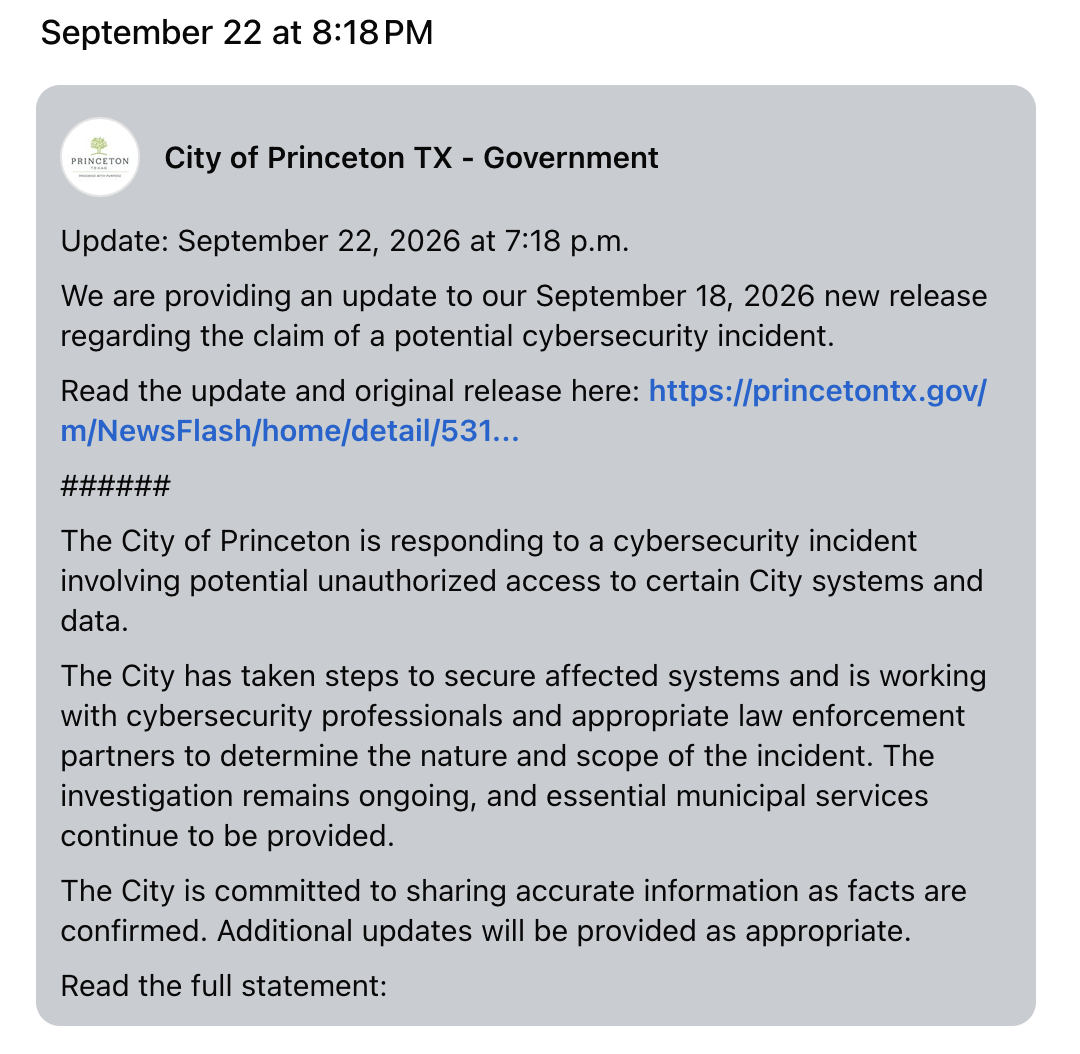
The city’s Facebook post retains its original Sept. 18 statement beneath links added for the Sept. 22 and Oct. 5 updates. Those revisions document one evolving public communication. The change from preliminary negative reviews to confirmed exfiltration reflects developing forensic findings; it does not establish concealment.

Current status

On Oct. 5, the city said essential services operated normally and its investigation continued. Once the review identifies affected people and information, the city plans to provide required notifications, identity protection and credit monitoring. That statement does not provide a full technical all-clear or a restoration date for every affected system. The Princeton Herald’s Oct. 8 report quoted Mayor Eugene Escobar Jr. saying the city was still determining affected systems and people and would contact impacted parties directly with guidance. Continuing investigation and notification work do not establish continuing operational disruption.

Threat actor and claim

Listed as: City of PrincetonSource: other

Claim details

RansomLook lists the City of Princeton, Texas, under INC Ransom, identifying princetontx.us and Collin County. The entry displays Sept. 16, 2026, but whether that date marks publication or tracker discovery has not been independently established. GalaxyWarden reported the listing Sept. 16.

Princeton confirmed data theft but has not attributed it to INC Ransom. The group’s responsibility and ransomware encryption remain unconfirmed.

Organizations involved

Impacted location

  • Princeton, Texas

    Affected city government’s physical anchor; no facility-specific downtime asserted.

    Municipal government’s service remit; does not assert citywide service disruption.

Sources

City of Princeton Listed by INC Ransom Ransomware Group

GalaxyWarden’s Sept. 16 report names INC Ransom as claiming City of Princeton, Texas, and alleged internal data theft. It explicitly labels the claim unverified and cites RansomLook.

City Investigating Potential Unauthorized Access to Systems and Data

Princeton disclosed potential unauthorized access on Sept. 18. A Sept. 22 update reported two reviews had found no evidence of a breach at that time. On Oct. 5, the city confirmed exfiltration of confidential and personally identifiable information and said essential services continued normally.

City of Princeton cybersecurity incident statement and updates

The city described potential unauthorized access, steps to secure affected systems and continuing essential municipal services. The edited post links to the city’s Sept. 22 and Oct. 5 updates.

Sept. 21 City Council emergency supplemental notice

The emergency notice described an active cybersecurity incident affecting critical city IT and communications systems. It provided for immediate consideration of response, recovery, security, remediation, emergency contracts and spending to protect city operations.

Princeton investigates potential cybersecurity incident

NBC 5 reported a group’s claim to city file-server data and a 10-day deadline to make contact before publication. A cybersecurity professional described the claimed material; the city disputed the evidence then available and said essential services continued.

Data stolen in city cyberattack

The Herald reported confirmed confidential/PII theft, continuing investigation and normal essential services. Mayor Eugene Escobar Jr. said affected parties would receive direct guidance. It also reported a resident’s Sept.28 allegation of unauthorized purchases with a card he held on file with the city; the report did not establish that the incident caused those purchases.

RansomLook INC Ransom listing: City of Princeton

RansomLook lists City of Princeton under INC Ransom with a Sept. 16, 2026 date, princetontx.us and a location in Collin County, Texas. The listing identifies municipal government as the sector.

See something that needs correction?

Signed-in members can report an error, update, or missing source.