Skip to content

INC Ransom

Ransomware Group25 claimsLast activity:

Overview

INC Ransom is a financially motivated ransomware-as-a-service operation that emerged in mid-2023. A joint advisory from the Australian Cyber Security Centre, CERT Tonga and New Zealand’s NCSC describes a division of labor in which affiliates conduct intrusions and deploy the ransomware, while the core operation maintains extortion infrastructure and handles payments. The group remained active through at least 2025, but public reporting about technical overlap with Lynx and older ransomware families does not by itself establish a common operator or confirmed rebrand.

Activity and targeting

INC Ransom affiliates have compromised organizations in multiple countries since 2023. The joint government advisory says earlier activity concentrated on the United States and United Kingdom and that targeting increased across Australia, New Zealand and Pacific island states from early 2025; it also reports a disproportionate focus on health-care organizations. Trend Micro’s 2024 research likewise found health care prominent in its telemetry and leak-site sample, alongside education, nonprofits, construction, professional services and manufacturing. Leak-site entries represent the actor’s claims and should not be treated as independently verified victim counts.

Methods and operational characteristics

Observed access routes include compromised or purchased credentials, spear-phishing and exploitation of known vulnerabilities in internet-facing systems. In one early incident, Huntress observed an operator using a compromised account and RDP, staging files with 7-Zip, installing MEGASync, accessing credentials and moving laterally before distributing the encryptor with WMIC and PsExec. The government advisory also documents the use of legitimate utilities such as 7-Zip, WinRAR and rclone for staging and exfiltration, underscoring that affiliate tradecraft can vary between intrusions.

INC Ransom uses double extortion: affiliates may steal sensitive data and encrypt systems, after which the operation threatens publication through a Tor-based data-leak site to pressure victims to pay. Trend Micro analyzed Windows and Linux variants and reported capabilities including partial or full file encryption, process termination and attempts to delete shadow copies. Encryption and data theft should still be assessed separately in each incident; an INC Ransom claim does not establish that either occurred.

What type of group is it?

INC Ransom is best characterized as a financially motivated cybercriminal service and affiliate network, not as a single intrusion team with an invariant playbook. That structure means access methods, tooling and target selection may reflect individual affiliates as much as the core operators. The reviewed sources do not publicly identify the people directing the operation, establish their jurisdiction or support state sponsorship.

Incident claims

Mississippi Institutions of Higher Learning network security incident

Incident date: Source: otherDiscovered:

Claim details

Breachsense’s monitoring entry reports an INC_RANSOM claim naming mississippi.edu and lists Oct. 12 as its discovery date, with leak size unknown. No authentic actor post or supporting sample was available in the reviewed entry. Connection to the September 2026 incident is low confidence; this claim does not establish ransomware encryption, data theft, actor responsibility, or a new October attack.

Sangre de Cristo Electric Association network intrusion

Incident date: Source: INC Ransom leak site (DysruptionHub screenshot)Published: Discovered:

Claim details

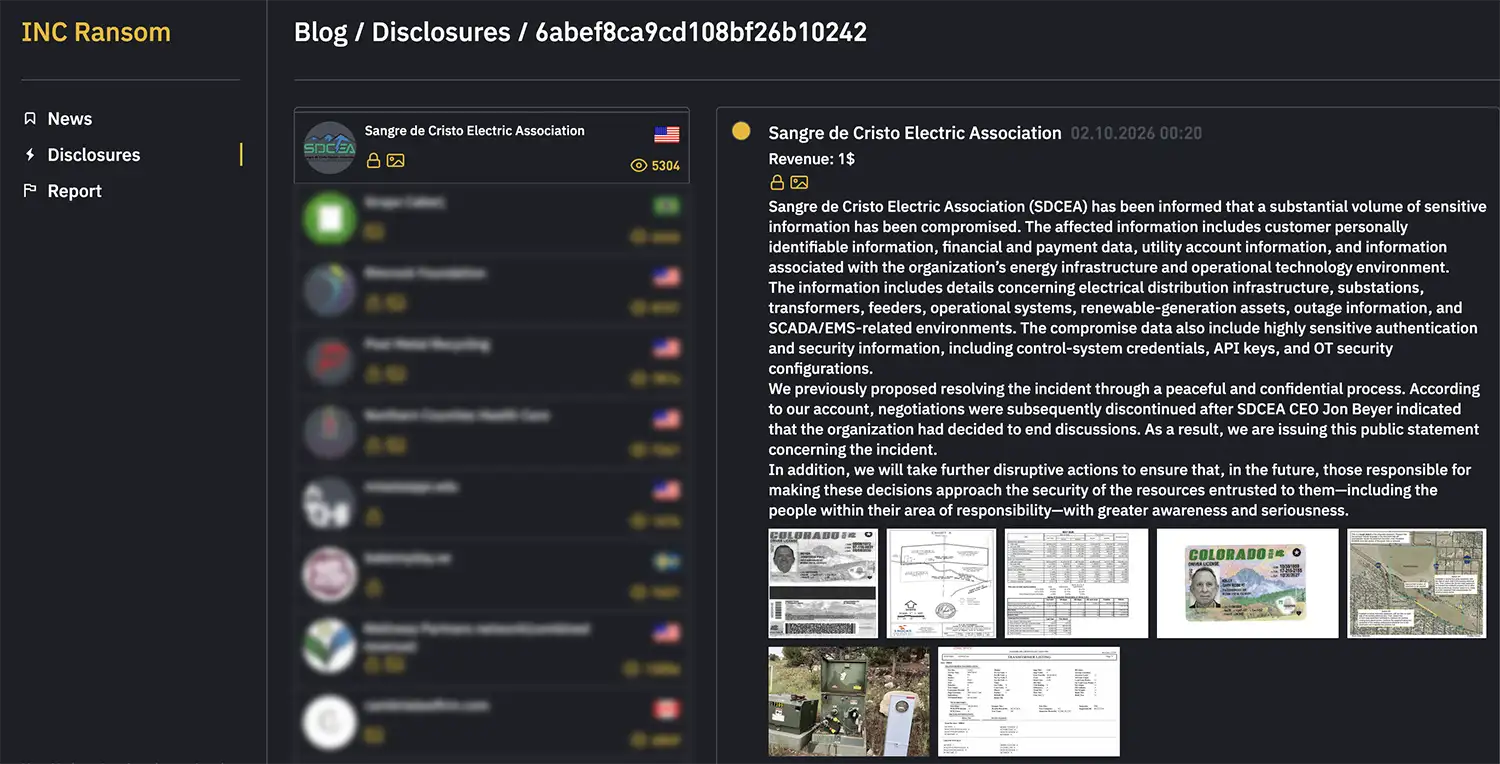
DysruptionHub reviewed the group’s own disclosure screenshot naming Sangre de Cristo Electric Association, displaying 02.10.2026 00:20 (time zone unspecified), disclosure ID 6abef8ca9cd108bf26b10242. INC Ransom alleges customer personal, financial/payment and utility-account data; electrical infrastructure records concerning substations, transformers, feeders, renewable generation, outages and SCADA/EMS environments; and control-system credentials, API keys and OT security configurations. Visible purported samples include identification documents, technical drawings, tabular records, a map/annotated aerial image and equipment photographs. Samples and alleged data/credentials have not been independently authenticated. The group attributes ended negotiations to CEO Jon Beyer and threatens further disruptive action; SDCEA has not corroborated those assertions or named INC Ransom. SDCEA says electricity was unaffected, payment and phone services were restored, and member payment information was not stored on the compromised local network. published_at records the date displayed on the claim page, not a verified publication instant or attack date. Direct post URL remains unknown. Screenshot: https://dysruptionhub.com/content/images/2026/10/sdcea-inc-claim.webp ; reporting: https://dysruptionhub.com/sangre-de-cristo-colorado-cyber-intrusion/

North Slope Borough School District cyber incident

View public claim
Incident date: Source: otherPublished:

Claim details

INC Ransom’s disclosure page lists nsbsd.org, the North Slope Borough School District domain, and displays 27.09.2026 07:45 beside the entry; the time zone is unspecified. SOCRadar and DeXpose reported the listing Sept. 28. DeXpose described a threat to publish data unless the district made contact. The listing is an actor claim, not proof that INC Ransom caused the Sept. 8 phone outage, encrypted systems, or obtained or published district data. The district has not identified an attacker.

Westfield Public Schools cyber incident

View public claim
Incident date: Source: ransomware.livePublished: Discovered:

Claim details

INC Ransom’s listing for Westfield Public School District showed an update at 2:33 p.m. UTC Sept. 2, 2026, adding a tranche of files the group claimed it stole from the district. Sample documents displayed with the post included employee Form W-2 wage and tax statements. The district has not confirmed the group’s attribution, the authenticity of the files or a data breach.

Lansing Urgent Care network-access incident

View public claim
Incident date: Source: ransomware.livePublished: Discovered:

Claim details

Ransomware.live records an INC Ransom leak-site listing naming Lansing Urgent Care at 6:25 p.m. UTC Aug. 17, 2026. Screenshots attributed to the listing show a 2015 safety data sheet for a third-party skin-care product, one page of a Lansing Urgent Care business-associate agreement and one page of an apparently incomplete employee nondisclosure agreement. The safety sheet contains no visible Lansing Urgent Care identifier, and the other documents are administrative rather than patient or clinical records. The images substantiate that INC displayed material it associated with the provider but do not authenticate the documents, establish that they were private, show how they were obtained or prove access to Lansing Urgent Care’s current network. WILX published the provider’s statement about an outsider’s access attempt and system shutdown about 24 hours after the claim. The timing and exact victim match make the claim likely related, but Lansing Urgent Care has not attributed the event to INC or confirmed ransomware, data theft or encryption.

Acworth cyber incident followed by INC Ransom claim

View public claim
Incident date: Source: ransomware.livePublished: Discovered:

Claim details

INC Ransom listed the City of Acworth’s official domain July 2, 2026, claimed to have obtained municipal data and threatened release if the city did not make contact. Public reporting said the listing included alleged samples. Acworth has not confirmed the actor, authenticity of the samples, data theft, encryption, a demand, negotiation or payment.

Meriden municipal network disruption and INCRansom claim

View public claim
Incident date: Source: otherPublished:

Claim details

INC Ransom listed meridenct.gov March 26, 2026. Later reporting on city notices acknowledges unauthorized network access and identifies ransomware, but does not attribute the event to INC Ransom or independently confirm encryption, exfiltration or publication.

Pennsylvania attorney general ransomware disrupted litigation

Incident date: Source: ransomware.liveDiscovered:

Claim details

INC Ransom claimed the Pennsylvania Office of Attorney General attack. Comparitech reports a Sept. 20, 2025 claim; MCP discovered it Sept. 21 at 00:46:34.134629 UTC. Original post timestamp was not independently verified. Claimed 5.7 TB, sample authenticity and FBI-network-access boast remain unverified. The victim confirms encryption to force payment and says it paid nothing; it has not verified INC attribution. Existing claim repaired without duplication.

University of St. Thomas–Houston cyberattack

Incident date: Source: ransomware.liveDiscovered:

Claim details

INC Ransom claimed the Houston university using stthom.edu and alleged 1.8 TB of stolen data, with samples. Comparitech’s page updated Sept. 4, 2025 describes the prior-day claim but no independently verified original post timestamp. Later Chronicle reporting independently examined part of a published record cache, supporting exposure without verifying the claimed volume, encryption or INC’s responsibility. No victim attribution or ransom/payment finding established. Existing claim repaired rather than duplicated.

Radford City Public Schools cyber incident

Incident date: Source: ransomware.liveDiscovered:

Claim details

Tracker reports an INC Ransom listing naming Radford City Schools and its verified domain rcps.org, threatening publication of an alleged 100 GB of sensitive, medical and personal data. Same entity identity is supported; responsibility for the June 2025 incident, theft, volume, data categories and encryption are unconfirmed. Discovery date is not attack or original publication date.

City of Durant ransomware attack

View public claim
Incident date: Source: ransomware.liveDiscovered:

Claim details

INC Ransom claims the city as a victim, alleges more than 800 GB of stolen data and threatens publication after a 48-hour deadline. The listing’s description identifies the city address and durant.org. The city has not confirmed INC Ransom’s responsibility, the claimed volume or the final disclosure outcome. Tracker discovery is not an intrusion or verified original publication date.

Pierce County Library System ransomware incident

Incident date: Source: ransomware.liveDiscovered:

Claim details

INC Ransom listed the library’s exact former domain. Independent reporting described the group’s 1.94 TB allegation and purported document samples. The library confirmed unauthorized access and data theft but did not independently establish INC’s responsibility or the claimed volume. Lead discovery is not an original publication or attack date.

Ahold Delhaize USA cyberattack disrupts grocery services

Incident date: Source: BleepingComputerDiscovered:

Claim details

BleepingComputer reported April17,2025 that INC Ransom had listed Ahold Delhaize the previous day and posted alleged document samples. April17 is the dated reporting observation; exact original actor publication time is not verified here. The company’s response confirmed file theft but declined to confirm ransomware involvement. This is an unconfirmed operator claim: it does not prove encryption, a payment, initial access method or validity of every alleged sample. LiveMCPcanonicalname/domain/USAname searches returnedzero, which does not erase this accessible reportedclaim. Preserve the independently researched canonicalINCactor and its sources.

Taylor Regional Hospital uses paper charts after cyberattack

Incident date: Source: ransomware.liveDiscovered:

Claim details

INC Ransom claimed the Georgia hospital and posted images described as stolen documents, according to Comparitech’s Jan. 17, 2025, report. The hospital had not verified the claim. The tracker observed the listing at the timestamp recorded here; it does not establish the original actor-post time or attack date. Alleged sample contents, exfiltration, ransom amount and payment remain unverified. The earlier named association official’s report of an attempted ransomware attack does not establish that INC caused it or successfully encrypted files.

Albemarle County ransomware attack

Incident date: Source: other

Claim details

Information Charlottesville, citing July 14 Daily Progress reporting, identifies INC Ransom in connection with the county ransomware incident. The county’s reviewed notices do not name the actor. A separate INC Ransom listing names k12albemarle.org; that school-domain listing does not independently establish county-government attribution or a county theft volume. Responsibility remains unconfirmed.

City of Princeton cybersecurity incident

Incident date: Source: other

Claim details

RansomLook lists City of Princeton under INC Ransom, with princetontx.us and Collin County, Texas. Its entry displays Sept. 16, 2026; the date’s publication/discovery semantics are not independently established. GalaxyWarden’s Sept. 16 report describes the listing. The city has not attributed its confirmed data theft to INC Ransom. Actor responsibility and ransomware encryption remain unconfirmed.

City of Thomasville ransomware attack

View public claim
Incident date: Source: other

Claim details

INC Ransom claimed the City of Thomasville June 2025 incident. Comparitech reported a 250 GB allegation and purported document samples; Cybernews reported 260 GB and a July 1 listing. The conflicting volumes, sample authenticity and INC attribution are unverified. The mayor separately acknowledged data removal and corruption without identifying INC or validating either volume. Original claim publication timestamp and direct leak-post URL remain unverified.

Anne Arundel County ransomware attack

Incident date: Source: other

Claim details

Eye On Annapolis attributed the February 2025 incident to INC in an undated update to its Feb. 22 report. The outlet also reported messages received in the county alleging that terabytes of data had been released on a site called incblog. These are secondary allegations; the reviewed evidence does not independently verify an actor-controlled victim listing, INC’s responsibility or a public data release. The county’s May 15 findings confirmed ransomware and unauthorized access from Jan. 28 through Feb. 22, but did not name INC. The current county incident page reports no indication of public release. The original claim’s publication and discovery dates remain unverified. Current tracker searches return a Rhysida claim from October 2026 concerning a separate incident; that claim does not substantiate this 2025 attribution. No ransom demand or payment has been verified.

Impacted organizations

Impacted locations

Sources