Analyst assessment
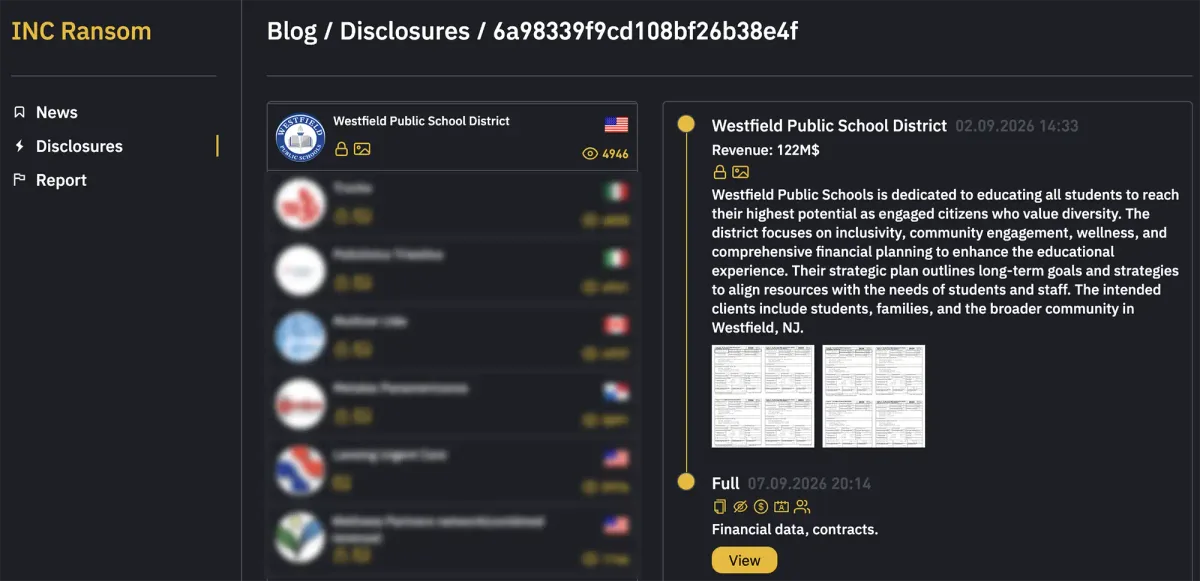
DysruptionHub assesses with high confidence that Westfield Public Schools experienced a disruptive cyber incident beginning Sept. 1, 2026. The district’s Sept. 1 notice documented a district-wide phone and network outage across all schools and offices, while an INC Ransom listing indexed by ransomware.live on Sept. 2 provides a stable external cyber claim naming the district. Under the registry’s evidence model, that stable named claim confirms an external cyber signal; it does not confirm ransomware deployment, encryption, data theft or INC Ransom’s responsibility.
The district initially said a networking hardware failure caused the outage. Its Sept. 2 update instead described a technical investigation with outside information technology experts and said systems would remain inaccessible until they could be restored safely. In a Sept. 3 update, the district said the cause remained under investigation, acknowledged online claims and said those claims were being reviewed without speculation. The evolution from a hardware explanation to an open investigation is material, but it is not an official cyber or ransomware confirmation.
Operational significance
The outage disabled internet and Wi-Fi, online instructional tools, district and school phone lines, and the student information system, including parent portals, online attendance and gradebook access. The Sept. 2 notice also identified affected clocks. Schools remained open, but teachers shifted to print materials, discussion, writing and other activities that did not depend on network connectivity, and administrators used contingency communications.
The impact extended across district schools and offices rather than a single building. The mayor’s Sept. 4 public-safety update said emergency-services communications remained available through a method independent of school telephone systems. The evidence therefore supports material educational and communications disruption but not a school closure, emergency-response outage or town-wide network failure.
Recovery and current status
The district’s Sept. 15 community update documented substantial but incomplete recovery. Intermediate and high school students had regained Chromebook access, but elementary Chromebook-cart onboarding continued. Parent Portal access, used for student-information review and electronic absence reporting, was expected by the end of Sept. 16. This was a target, not confirmation of restoration.
Superintendent Raymond González said user-facing services had largely returned and ended daily districtwide restoration updates, returning technology communications to school-based channels. External cybersecurity and information technology specialists continued their investigation and technical work. The specific remaining device and portal limitations mean this was not a comprehensive all-clear.
The Sept. 15 notice is the last dated record of operational limitations. No reviewed later notice confirms complete restoration or establishes how long the remaining limitations lasted.
As of Oct. 19, the incident is presumed resolved because 34 days have passed since the latest supported operational-impact observation and no newer continuing disruption was established in the review. This is an assessment of operational status, not confirmation of complete restoration. The exact restoration date remains unknown.
Data impact and attribution
Unavailable student-information systems and parent access establish an availability impact. INC Ransom’s existing public claim and apparent document samples remain unverified claims of data theft, not independent confirmation of exfiltration or the group’s responsibility. The district has not publicly confirmed ransomware deployment, encryption, a data breach, ransom payment or the access vector.
Confidence and uncertainty
Confidence is high in the documented district technology disruption. The named INC Ransom claim provides concrete external cyber evidence, but ransomware deployment, data theft and the group’s responsibility remain unconfirmed.
Analytic gaps
The initial access route, complete compromised-system and data scope, actor responsibility and final restoration date remain unknown.