Analyst assessment
We reported that a cyberattack disrupted the Town of Andover, Massachusetts, and Andover Public Schools’ shared technology environment beginning Aug. 13. Most connectivity returned Aug. 17, but newly released records document additional restoration through Aug. 21. Town Manager Andrew Flanagan confirmed in an email first reported by Andover News on Aug. 22 that the disruption resulted from a cyberattack. The Town activated its cyber incident response procedures, temporarily took external email offline and engaged independent cybersecurity professionals.
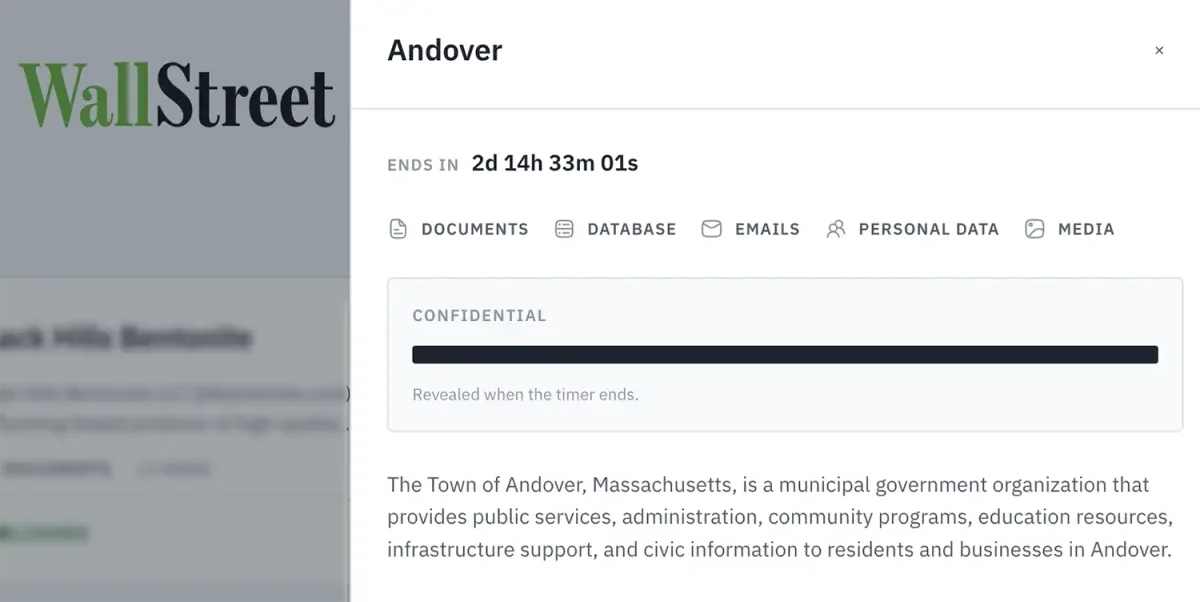
Wallstreet later listed Andover on a data-leak site. Ransomware.live indexed the claim Aug. 30 and reproduced a description identifying the Town of Andover, Massachusetts. A captured image of the listing asserted possession of documents, databases, emails, personal data and media and displayed a countdown before a redacted confidential item would be revealed. The stable claim is treated as concrete external cyber evidence, not as proof of ransomware, data theft or actor responsibility.
The exact municipal identity and the claim’s timing support a low-confidence association with the Aug. 13 incident. No victim statement, technical indicator or independently verified evidence links Wallstreet to the intrusion. The public record does not support confirmed ransomware. Red Piranha reported that Wallstreet operates a data-leak site but that public technical reporting had not established an encryptor, ransomware note, code lineage or Wallstreet-specific malware indicator.
Operational significance
The incident disrupted shared systems serving municipal departments and the public school district. Restoration was staged rather than complete after four days. The Town’s Aug. 13 notice said an internet-connectivity problem could disrupt services and prevent residents from reaching staff by email. Andover Public Schools reported the same day that the connectivity problems affected several services; a Friday update said internet and email disruptions continued Aug. 14 while the information technology department worked to restore service.
Town buildings remained open, telephones continued working, and public safety agencies, utilities and other infrastructure were not interrupted. The disruption nevertheless limited access to some municipal services, temporarily disabled external staff email, interfered with online bill payments and delayed Andover Public Schools’ release of teacher assignments shortly before the school year. The school impact is an effect on district administration and family-facing services, not a documented interruption of classroom instruction.
The Town and school district use a unified information technology organization and shared network infrastructure. The affected location is Andover, the municipality served by both organizations. Essex County is included only as the administrative parent of the municipality and is not modeled as a countywide impact area.
Internal restoration notices released in response to a public-records request show wired internet, email and several business systems returning Aug. 17; printing and Wi-Fi Aug. 18; library applications and online bill payments Aug. 19; and all Town and school shared network files Aug. 21. MUNIS, the financial system, was restored from a backup taken at midnight Aug. 12, requiring employees to re-enter work completed later that day. This establishes temporary data unavailability and recovery work, not permanent data loss.
Confidence and uncertainty
Confidence is high that the outage was cyber-related because the town manager expressly called it a cyberattack and described cyber-response measures. Confidence is low that ransomware or data extortion was involved and low that Wallstreet was responsible. Those judgments rely on the stable victim claim, the exact organizational description and temporal proximity, not on technical attribution or victim confirmation.
The available evidence does not identify the initial access vector, malware family or other attack mechanism. Public reporting states that it remained unclear whether Town or school data was accessed, copied or compromised. Wallstreet’s assertions do not independently establish encryption, exfiltration, a ransom demand or the authenticity and scope of the claimed data.
Andover News reported Sept. 25 that the Town signed agreements with cybersecurity firm Vector3 and outside counsel on the first evening of the attack. The released agreements estimated $30,105 in Vector3 fees and $9,500 in initial legal fees, with an additional $4,500 if specified notification services were needed, plus other possible expenses. These are contract estimates, not a verified total spent or a ransom payment. Ransomware-response and optional attacker-communication services in the contract do not establish that encryption, negotiations or payment occurred.
Disclosure posture
The Town initially characterized the event on Aug. 13 as a temporary internet-connectivity issue. The first located public cyber-specific explanation appeared Aug. 22, when Andover News reported the town manager’s Aug. 21 email confirming a cyberattack. Because that confirmation came from the affected organization before the Aug. 30 external claim, the incident is assessed as organization-first cyber disclosure.
Current status
The disruption remains presumed resolved because the Aug. 21 internal notice said critical Town and school services were fully operational and all shared files had been restored. The same notice said remote VPN access remained unavailable during a redesign and rebuild, with no estimated completion date. Full restoration of that residual service has not been publicly documented. The Aug. 17 public notice described earlier progress; the released Aug. 19 records establish that online bill payments subsequently returned. Aug. 21 is the latest documented operational impact, not Sept. 25, when the records were reported. No definitive incident end date is established.
The data-impact investigation remains open. Andover News reported Sept. 29 that Town Counsel Doug Heim told the Sept. 28 Select Board meeting investigators had not yet determined whether protected personal information was obtained or distributed, or who might require notification. He provided no timetable. This continuing forensic work does not itself establish a renewed service disruption.
Analytic gaps
The public record does not establish Wallstreet’s responsibility, the entry method, compromised hosts or accounts, malware, persistence, encryption, data access or theft, a ransom demand, actual response spending or the VPN restoration date. The Town’s Sept. 22 records response withheld investigative and other material and does not constitute a finding that no data was compromised. At the Sept. 15 Select Board meeting, the town manager said legal, insurance and cybersecurity considerations limited disclosure. The Town and school district have not publicly confirmed the Wallstreet claim.