Analyst assessment
Cedar Crest College identified a significant cybersecurity incident at approximately 7:45 a.m. July 13, 2026, affecting portions of its technology environment. The college’s official incident page identified FalconLink, FalconApp, campus network drives, OneDrive and other network- and cloud-based file-sharing systems as affected while it activated emergency response procedures and engaged external specialists.
In its latest dated update July 20, Cedar Crest said it continued to investigate the incident and securely restore system access. The college could not provide a definitive timetable for every affected service and directed users with account, login, device, email, network or application problems to its HelpDesk. DysruptionHub assesses with high confidence that malicious or unauthorized cyber activity caused material disruption to campus technology services.
Operational significance
The incident restricted access to applications and shared-storage services used for academic and administrative work. The July 20 notice is the last positive evidence that restoration remained incomplete. An August 18 retrieval of that unchanged notice did not establish that disruption continued on the retrieval date and therefore does not advance the operational-impact clock.
Current status
The incident is presumed resolved. Cedar Crest published a detailed orientation schedule for required programming and residential move-in August 20-23, and its academic calendar lists August 24 as the beginning of fall classes. No contemporaneous service warning, complaint or report of continuing material technology disruption was located.
Those signals do not prove that every affected system had been restored, and the college did not publish a definitive all-clear or recovery date. They do, however, weigh against presuming that a materially disruptive outage continued through the opening of the academic year. A continuing security investigation or an unchanged incident page does not by itself establish continuing operational impact.
Disclosure posture
Cedar Crest said some information may have been accessed or compromised, but it did not confirm unauthorized access or acquisition. It said affected individuals would be notified if the investigation established that notification was appropriate or required.
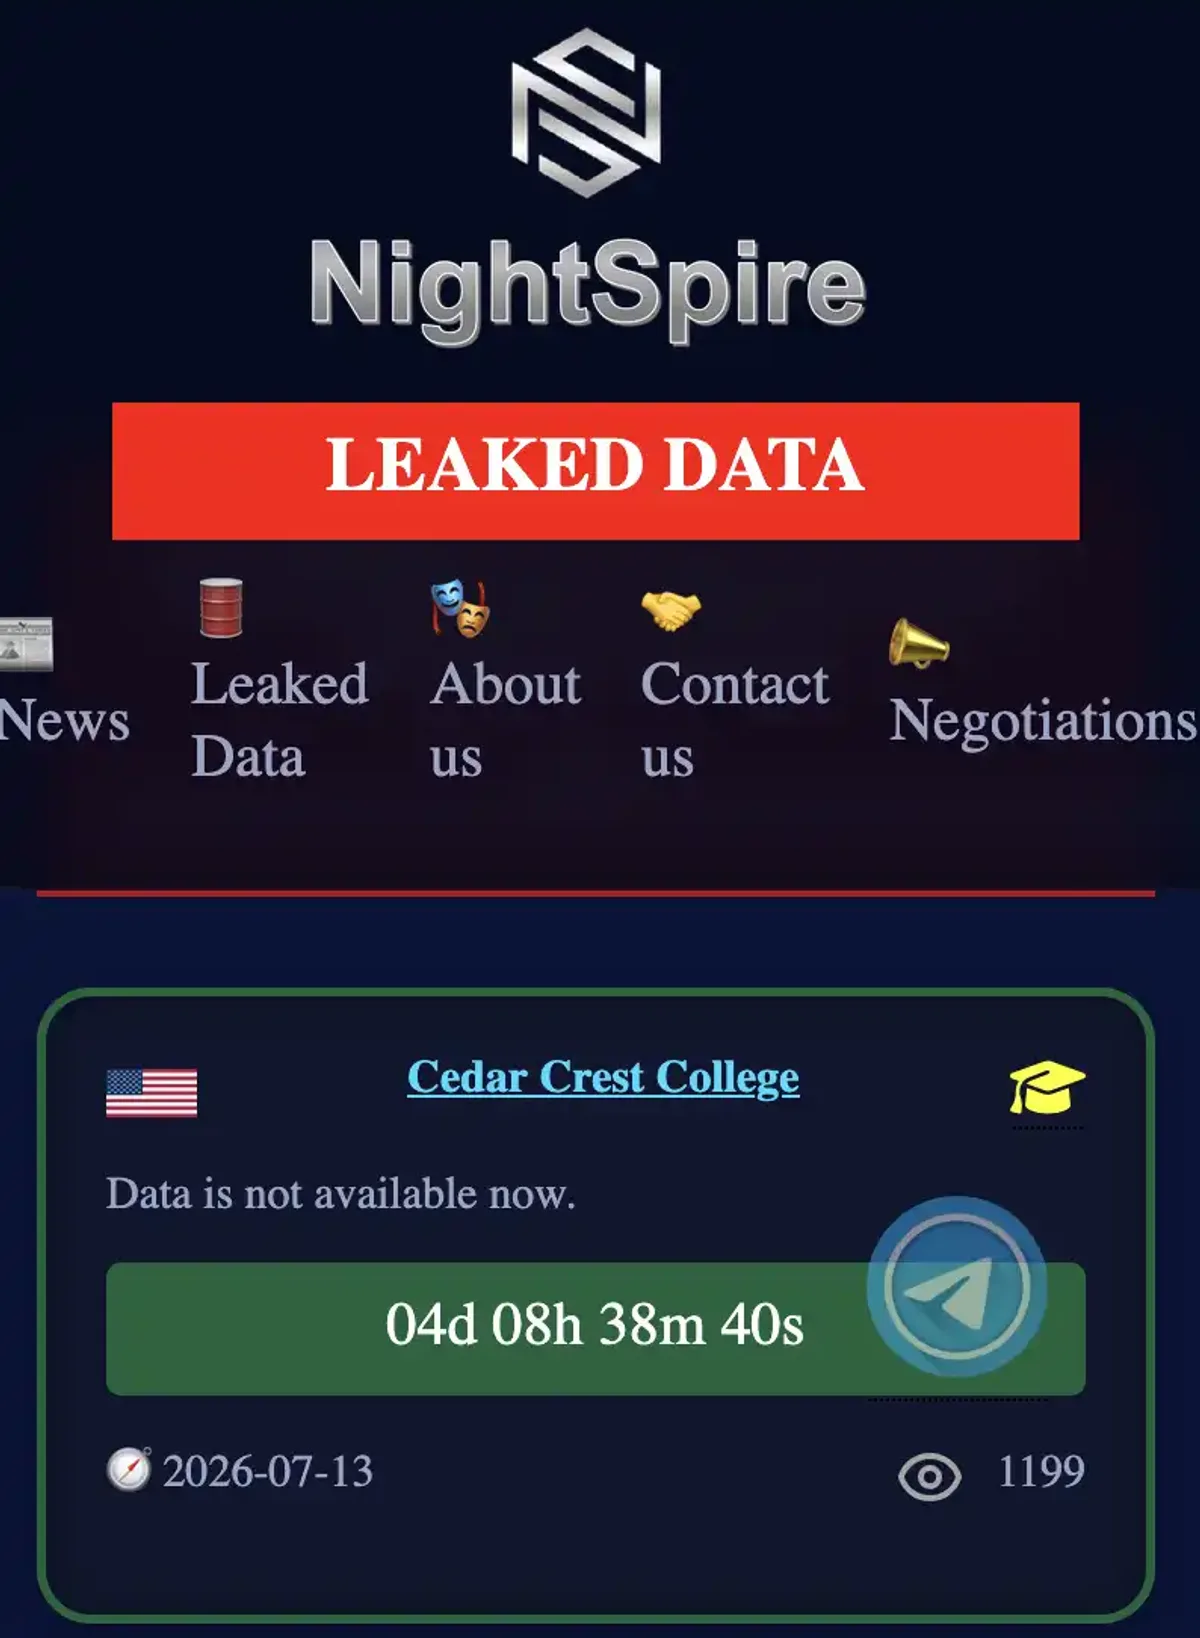
Ransomware.live recorded a NightSpire claim associated with Cedar Crest. Our report said the listing identified July 13 as the attack date but provided no description of allegedly stolen data. The college has not attributed the incident to NightSpire or confirmed ransomware involvement.
Confidence and uncertainty
Cyber and disruption confidence remain high because Cedar Crest directly confirmed the incident and named affected systems. Confidence in presumed operational resolution is medium because normal academic activity provides a meaningful counter-signal but no definitive all-clear or restoration date was published. Ransomware and NightSpire attribution confidence remain low.
Analytic gaps
The public record does not establish the initial access vector, intrusion start time, malware family, affected hosts, encryption status, backup impact, information involved, number of affected people or exact restoration date.