
Claim details
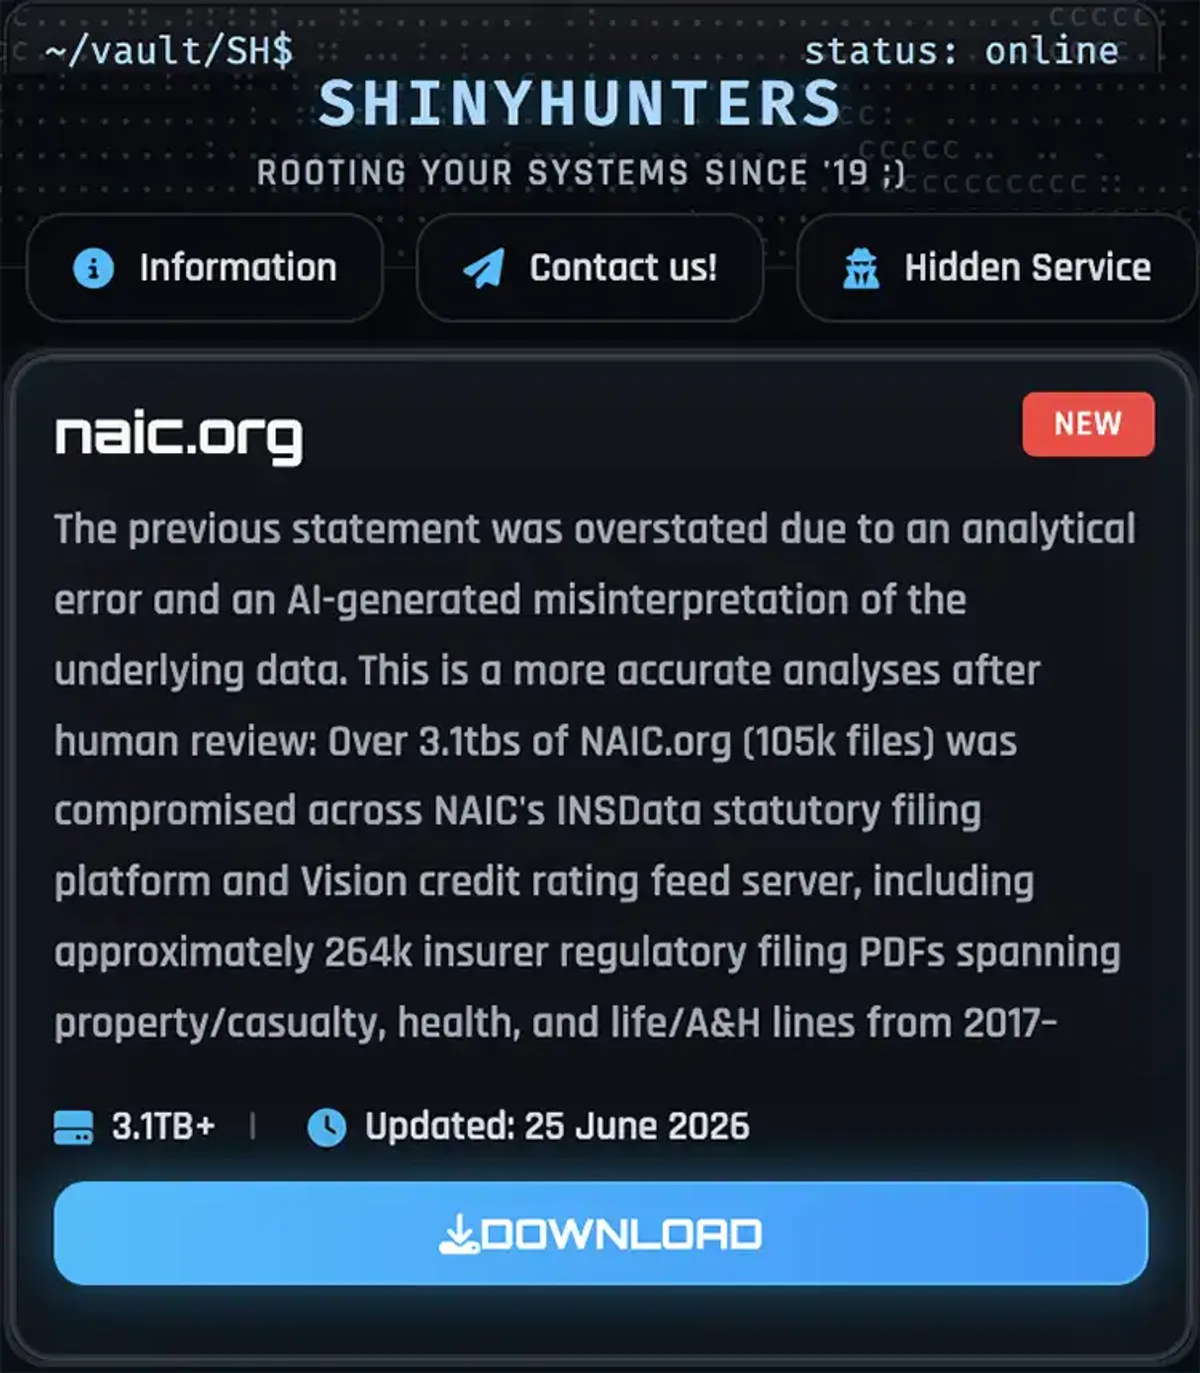
ShinyHunters claimed on its leak site that it obtained and published more than 3.1 TB of NAIC.org data. NAIC confirmed publication by the responsible party but did not publicly name the group or validate the claimed volume.
NAIC’s PeopleSoft intrusion involved data acquisition and publication and disrupted investment designations and invoice payments. Rating feeds resumed in August, and regular FE/PLR designation publication restarted Aug. 17. Operations remain presumed resolved; the online-invoice recovery date and conclusive actor attribution remain unknown.
The organization publicly identifies the event as cyber-related. The organization publicly documents the resulting service disruption.
Threats to publish or sell stolen data without evidence of encryption.
Unauthorized access to systems, accounts, networks, or data.
Exploitation of a software or hardware vulnerability to gain unauthorized access or execute malicious actions.
Data was copied, transferred, downloaded, or otherwise removed from the affected environment by an unauthorized party.
Stolen, exposed, or otherwise compromised data was publicly released, posted, distributed, or offered for download.
The organization could not process, receive, issue, reconcile, or record payments normally.
Business, financial, customer, administrative, or operational transactions could not be completed normally.
The incident caused operational effects at customers, affiliates, subsidiaries, partners, tenants, or other dependent organizations.
The actor explicitly threatened to publish or publicly release victim data or incident details.
The victim received a demand for payment in exchange for restoring access, decrypting systems, preventing disclosure, or stopping another threatened action.
The actor threatened to disclose, sell, distribute, or otherwise misuse stolen data unless the victim paid or complied with demands.
The victim was listed on a threat actor or ransomware data-leak site as an alleged target or nonpaying victim.
The actor published or released a substantial or complete set of allegedly stolen victim data.
DysruptionHub assesses with high confidence that the National Association of Insurance Commissioners experienced unauthorized access involving its Oracle PeopleSoft environment. NAIC’s security update says it detected the access June 11, 2026, and that information enabling temporary access to certain storage areas was used to acquire data later published.
Oracle’s CVE-2026-35273 advisory describes an unauthenticated, remotely exploitable PeopleSoft PeopleTools vulnerability that can permit remote code execution. NAIC attributed its incident to exploitation of the PeopleSoft zero-day and said it was part of a broader campaign.
Some credit-rating providers paused rating-symbol feeds after notification. Beginning June 18, NAIC suspended assigning and publishing designations derived from certain public or private ratings in AVS+. Its July 8 update supplied a second-quarter reporting workaround using June 17 data but did not announce restoration of the regular designation process. The July 8 operational update also described unavailable online PeopleSoft invoice payment.
NAIC said most operations had returned to normal and that major state regulatory platforms were unaffected. The confirmed residual effects were therefore narrower designation and payment exceptions rather than an organization-wide outage.
The incident remains presumed resolved. NAIC’s Aug. 18 update said all required rating feeds were being received and regular FE/PLR designations had resumed publication in AVS+ effective Aug. 17, with status updates in VISION and STS. It extended private-rating filing deadlines to account for the outage. This resolves the previously documented designation exception; the public page does not supply an online PeopleSoft invoice-payment restoration date.
An Oct. 13 notice said routine updates to the page were complete and future information would be posted if needed. That is a communication milestone, not renewed disruption or a precise all-systems end date. No newer operational-impact evidence was found through Oct. 22.
Confidence is high in vulnerability exploitation, unauthorized access, data acquisition, publication and operational disruption because NAIC confirmed those facts. Confidence is medium in ShinyHunters attribution because the group claimed the incident and independent reporting connected the claim, but NAIC did not name the actor. The evidence supports data-theft extortion rather than ransomware encryption.
The public record does not establish the intrusion start, dwell time, full affected-host inventory, lateral movement, complete published-data contents, ransom amount, negotiation history or conclusive attribution. Regular CRP-based designation publication resumed Aug. 17; the restoration date for PeopleSoft invoice payment remains unknown.
ShinyHunters claimed on its leak site that it obtained and published more than 3.1 TB of NAIC.org data. NAIC confirmed publication by the responsible party but did not publicly name the group or validate the claimed volume.
NAIC said a PeopleSoft security incident left insurer investment designations suspended and online invoice payments unavailable; it also said unauthorized access reached data storage areas and that ShinyHunters claimed more than 3.1 TB of data.
Oracle’s June 10 alert says CVE-2026-35273 affects PeopleSoft Enterprise PeopleTools 8.61 and 8.62, is remotely exploitable over HTTP without authentication, has a CVSS 3.1 score of 9.8, and can result in remote code execution.
Aug. 18 notice confirms rating feeds and regular FE/PLR designation publication resumed effective Aug. 17. Oct. 13 notice ends routine page updates. An invoice-payment recovery date is not provided.
BleepingComputer reported that ShinyHunters claimed the NAIC intrusion and published data after NAIC refused a ransom. The group revised its claim to 3.1 TB across about 105,000 files and acknowledged that an earlier inventory was exaggerated through AI hallucinations; NAIC disputed the broader system claims and reported no evidence of PII or financial-data exposure.
Signed-in members can report an error, update, or missing source.