

CivicPlus took its municipal website platform offline Wednesday over a PHP security vulnerability, disrupting customer websites including the city site for Naples, Florida.
The government software provider said the shutdown covered all versions of Web Open. Its Community Development software also faced disruptions, with version 3 offline and version 4 restored but under monitoring.
The company’s incident notice identified a vulnerability affecting PHP, software used to run websites. CivicPlus did not identify the specific flaw or say whether it had been exploited.
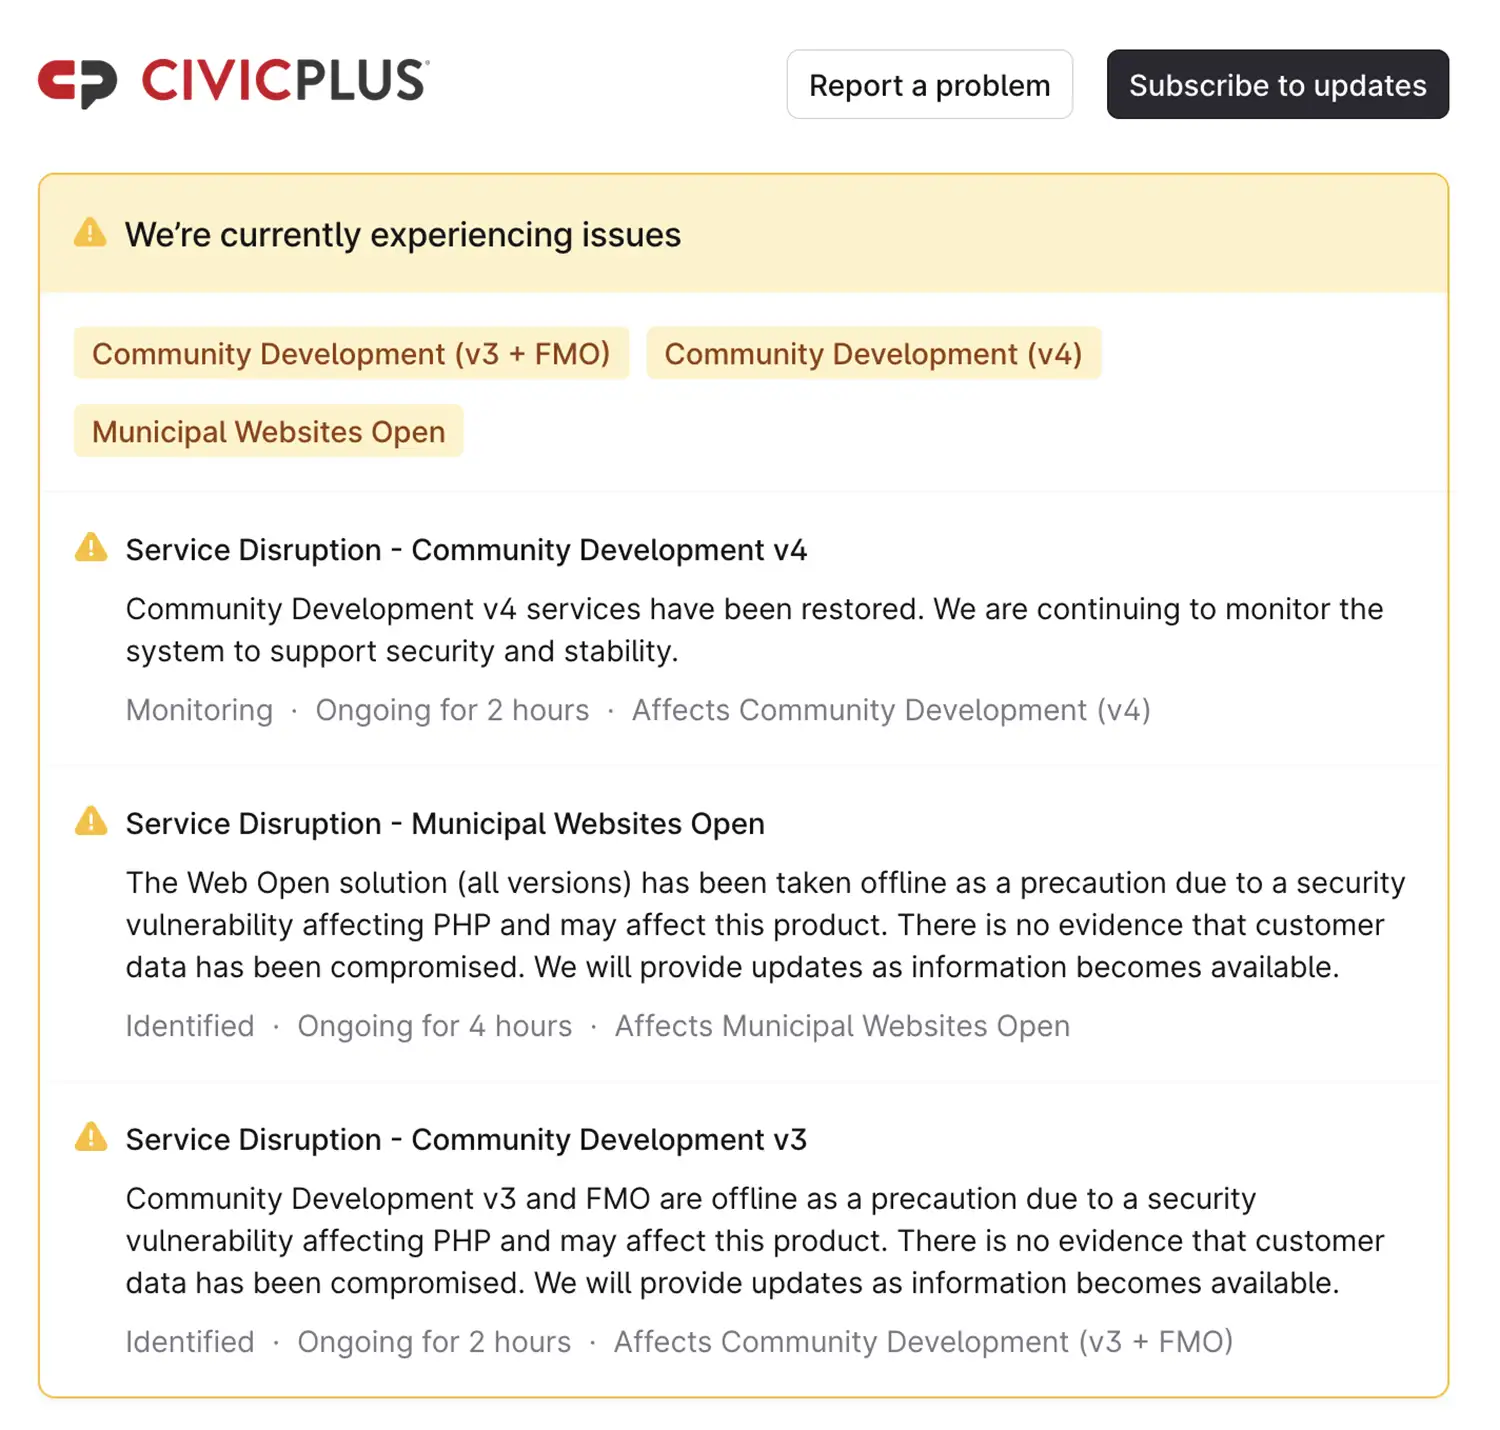
“There is no evidence that customer data has been compromised,” the company said.
Naples officials said CivicPlus had taken the city’s website offline over a “suspected security vulnerability” and was working to restore service, Gulf Coast News reported Wednesday.
Links to individual City Council agenda items through the city’s Granicus system were also unavailable, officials told the station. The city directed viewers to Naples TV for the meeting, and the station provided an alternate agenda document.

Chip in once
If this reporting helped you, a one-time tip helps cover hosting, tools and future investigations.

Support us monthly
A small monthly pledge keeps independent coverage and our reader tools online for everyone.
CivicPlus had not named all affected municipalities or said how many customers were affected.
Earlier this month, a cyberattack at Mississippi web host U.S.NEXT disrupted government websites and email, prompting counties to offer alternative access to information and services. U.S.NEXT confirmed an attack. CivicPlus described its shutdown as a precaution.
Web Open remained offline Wednesday afternoon, according to CivicPlus’ status notice. The company had not provided a restoration estimate.


