

The FBI’s recruiting website and application portal were unavailable for a second day Wednesday as the bureau investigated a hacking group’s claim of unauthorized access, disrupting online job searches and applications.
The FBI’s applicant guide says the public website describes positions and qualifications, while the separate portal lets candidates apply, upload documents and track applications.
During a Wednesday afternoon check, DysruptionHub found a maintenance notice on the application portal and a temporary-unavailability message on the recruiting website. Neither explained why the services were down. Reuters reported that both were unavailable Tuesday.
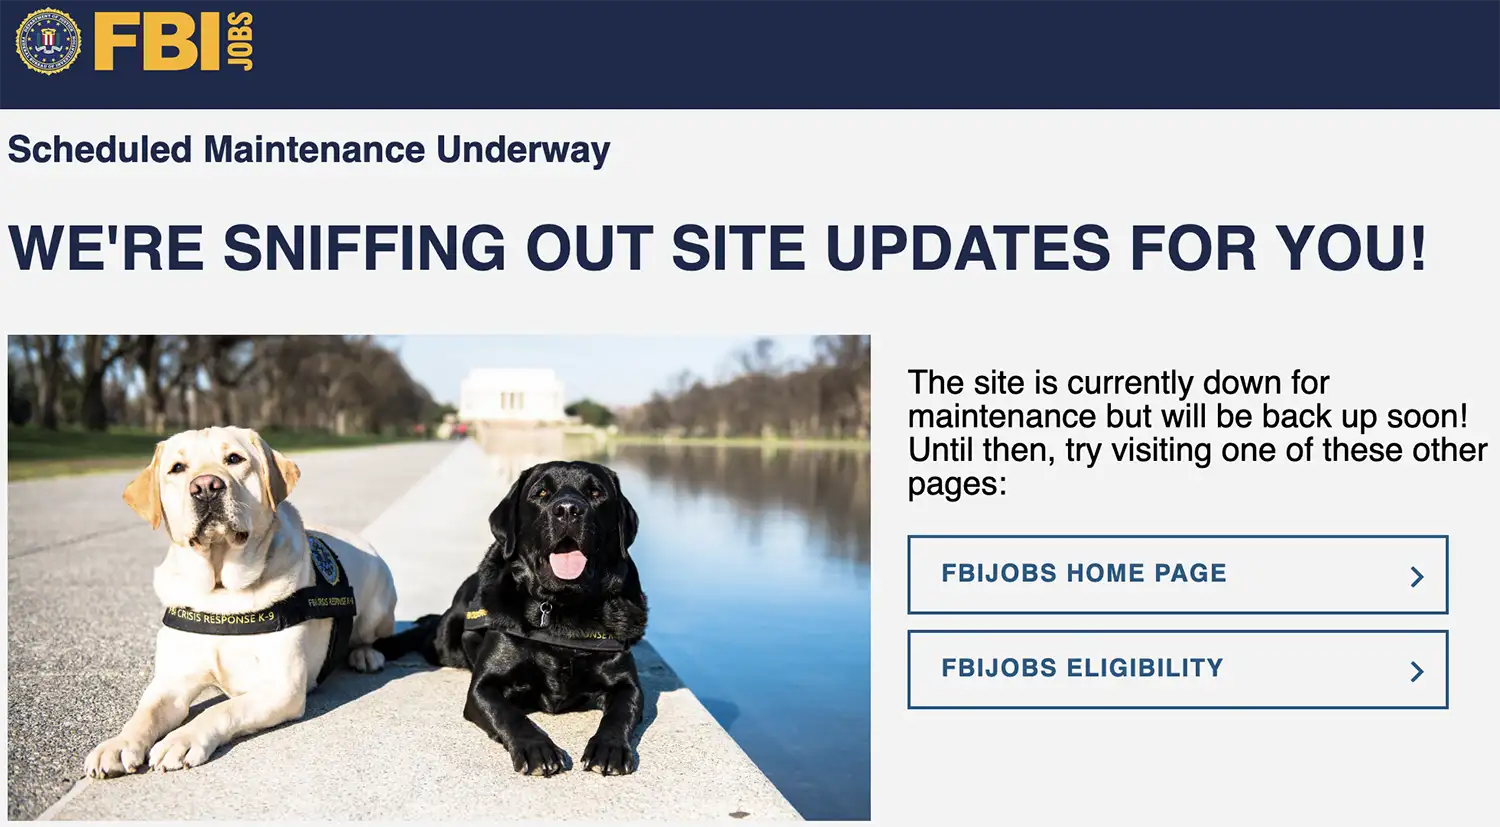
The FBI said Wednesday it was investigating a claim that its jobs portal had been compromised and employee information affected. It said it had not determined whether the alleged breach involved a third-party provider or its own systems.
ShinyHunters claimed it entered FBI systems and stole employee and applicant data. BleepingComputer reported that the group supplied an image purporting to show the application portal defaced. The outlet said it could not verify the group’s claims about a previously unknown Oracle PeopleSoft flaw, access to other systems or the amount of data taken.
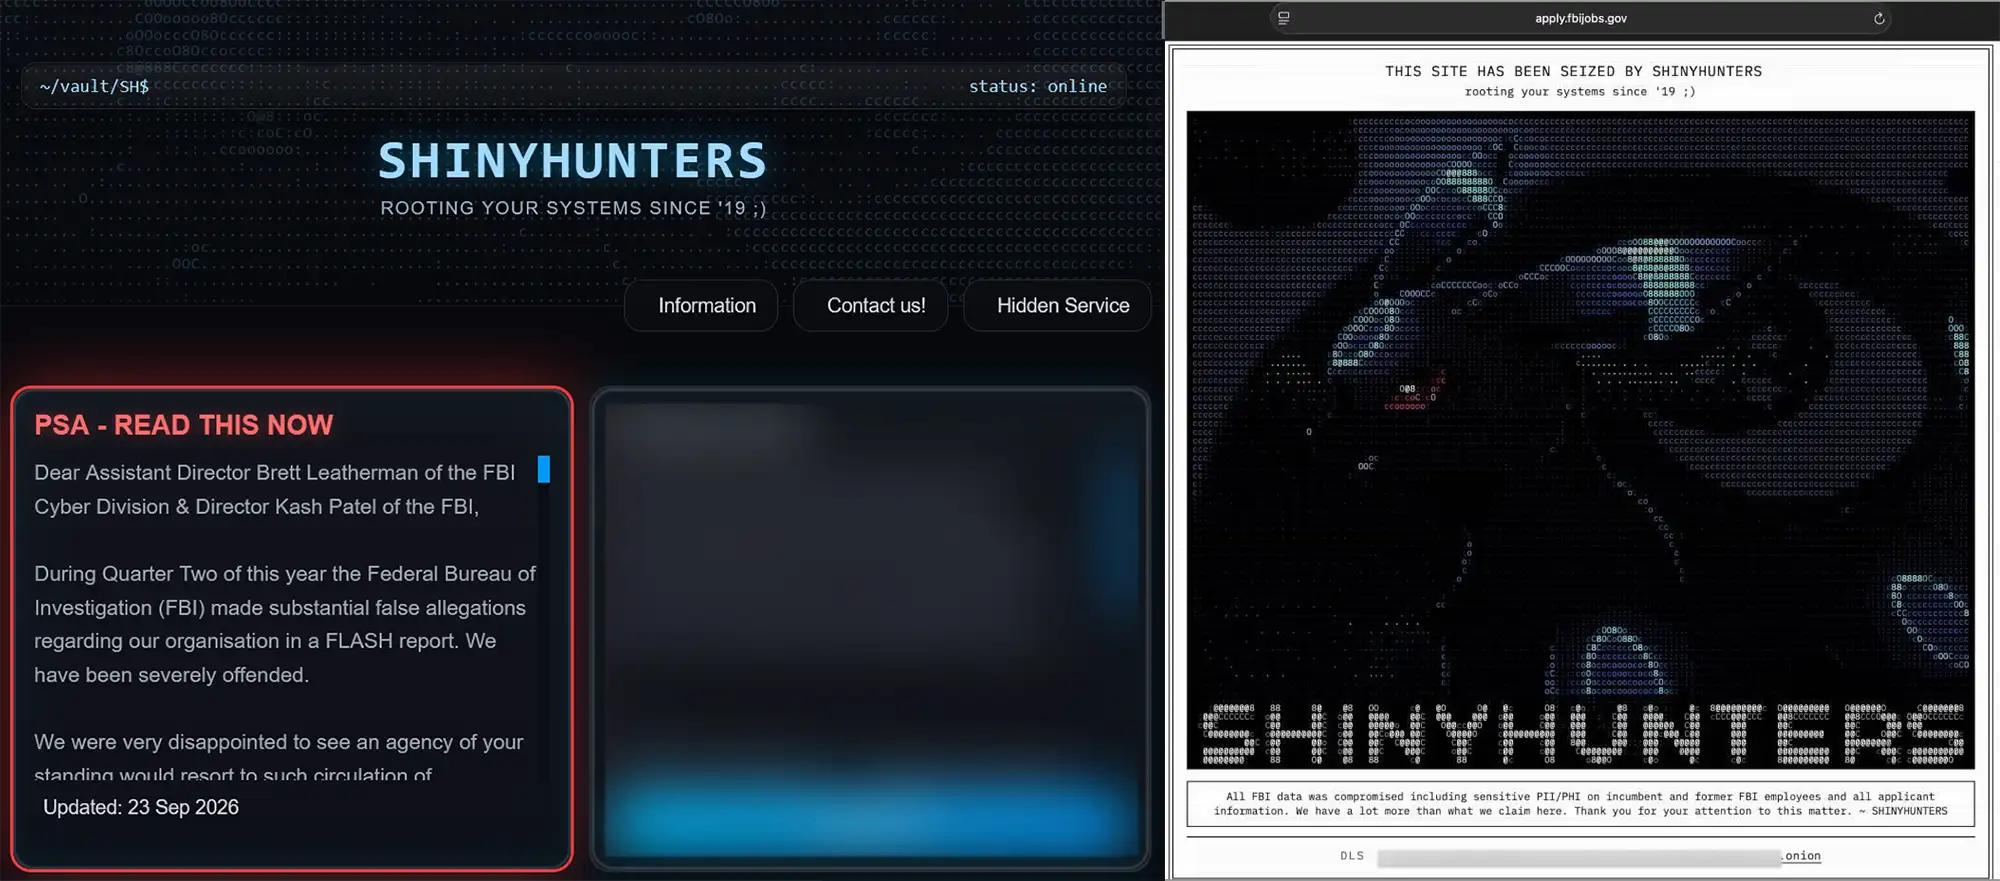
BleepingComputer documented a statement on ShinyHunters’ leak site, but DysruptionHub could not find the statement during a Wednesday check.
Reuters reported that it partially verified details in a sample of purported personnel records but could not establish where the data came from. Politico reported that two people with knowledge of the investigation said investigators considered the group’s claims credible. The FBI has not confirmed an internal breach or data theft.

Chip in once
If this reporting helped you, a one-time tip helps cover hosting, tools and future investigations.

Support us monthly
A small monthly pledge keeps independent coverage and our reader tools online for everyone.
In August, the ransomware group Qilin claimed an intrusion at ATF. The agency disconnected a standalone investigative system but said it retained its broader mission capability; it has not attributed the intrusion to Qilin. Public ransomware and data-extortion claims against federal agencies remain uncommon compared with attacks on schools, hospitals and local governments.
The portal’s notice gave no restoration time or guidance for applicants facing deadlines.


